Adrian Lamo’s Hacking Career Ended in the Chelsea Manning Case
Adrian Lamo gained fame through unauthorized network intrusions, then became a central and controversial figure after reporting Chelsea Manning.
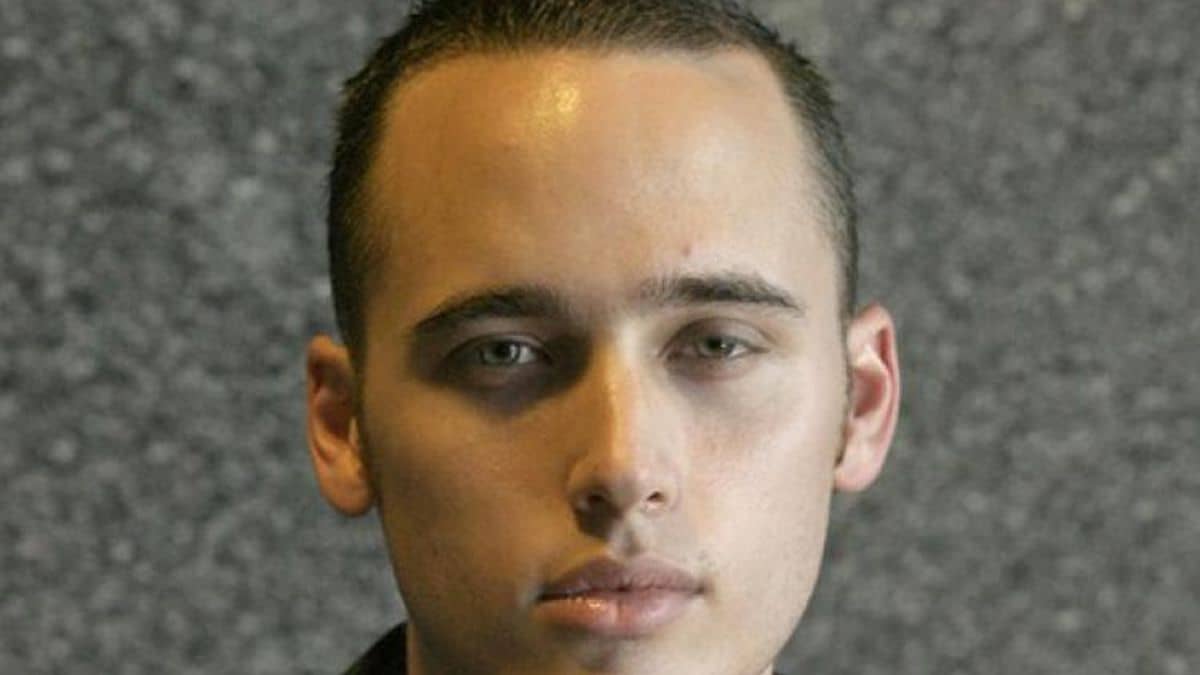
Adrian Lamo was called the “homeless hacker” because he travelled with a backpack and connected from libraries, cafés and public terminals. His unauthorized access to major networks made him famous; his decision to report Chelsea Manning made him permanently controversial.
The grey-hat years
Lamo entered systems belonging to companies including Microsoft, Yahoo and The New York Times. He sometimes notified organizations after finding weaknesses, but disclosure after access did not make the access authorized.
The Times intrusion led to federal prosecution. In 2004, Lamo pleaded guilty to a felony computer-crime count and received home detention, probation and a restitution order.
2002
New York Times intrusion
2004
Federal guilty plea
2010
Reported Manning’s disclosures
37
Age at his death in 2018
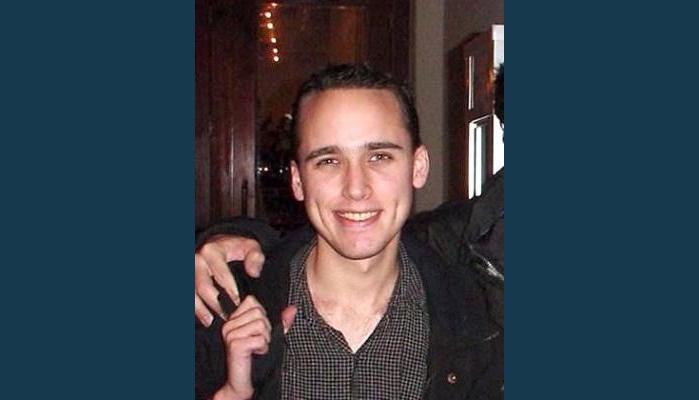
Adrian Lamo in a later portrait.
The Manning chats
In 2010, U.S. Army intelligence analyst Chelsea Manning contacted Lamo online and described providing classified material to WikiLeaks. Lamo shared the conversations with U.S. authorities.
He said he feared further disclosures could cause harm. Critics argued that he betrayed a vulnerable source who believed the conversation was confidential. The decision led directly into one of the most consequential leak prosecutions in U.S. history.
No simple label
“Grey hat” is often used for researchers who act without permission but claim a public benefit. Lamo’s career demonstrates why that label can obscure legal and ethical questions: who gave consent, what data was accessed and who bore the consequences?
Lamo died in Kansas in March 2018. A medical examiner could not determine the cause.
The geek lesson
Finding a vulnerability is only the beginning. Authorization, evidence handling, confidentiality and responsible reporting determine whether technical curiosity becomes legitimate security work—or harm.
The weekly question
From obsession to clarity — one original question every week.
We answer one noisy topic at a time, in full. No daily roundup, no thread bait — just the question, the principles, and the system.